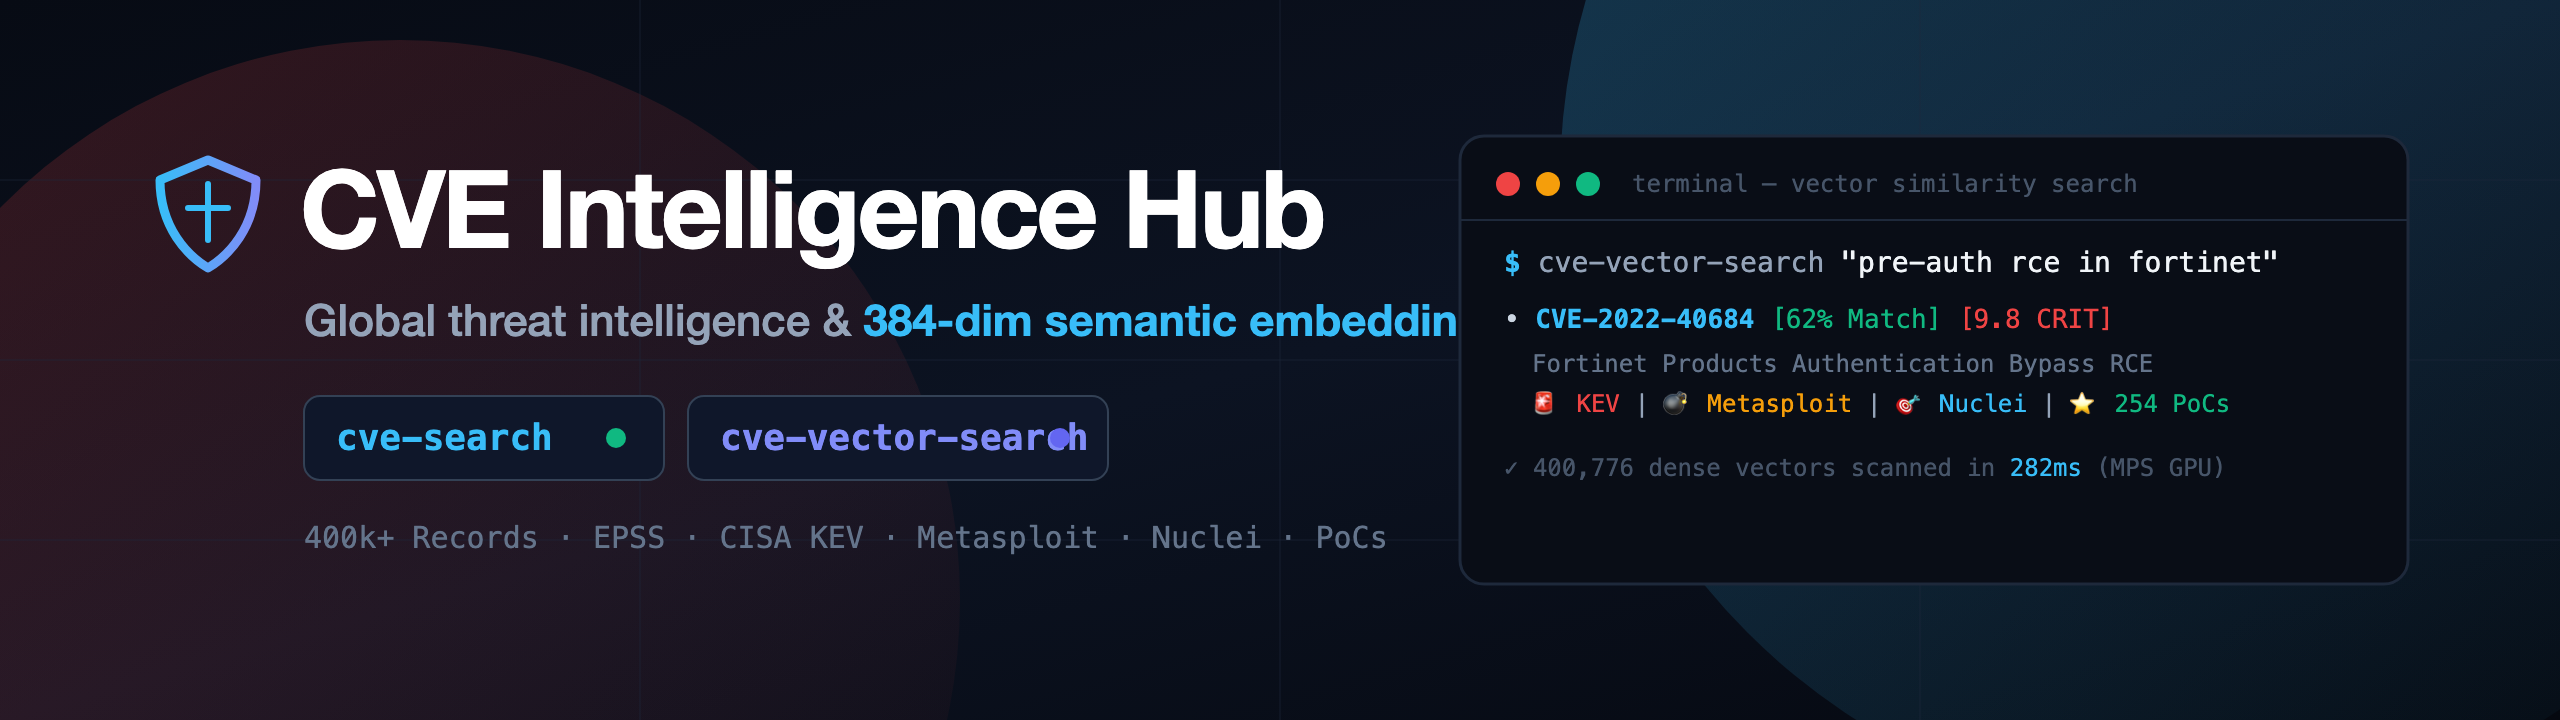
CVE Intelligence Hub
A self-contained, 100% offline threat intelligence search engine indexing all 400,000+ official CVEs (1999–2026) enriched with 384-dimensional dense semantic embeddings, CISA KEV active exploitation flags, FIRST EPSS exploit probabilities, Metasploit modules, Nuclei templates, and GitHub PoC repositories.
⚡ Zero API Keys & Offline
Runs entirely from local SQLite and memory-mapped NumPy matrices. No external API quotas, no rate limits.
🧠 384-dim Semantic Embeddings
Trained using all-MiniLM-L6-v2 on Apple Silicon Metal GPU for natural language query similarity.
🚨 CISA KEV + EPSS Scoring
Correlates theoretical CVSS severity with real-world active exploitation and 30-day exploit probabilities.
💣 Metasploit & Nuclei Mappings
Direct paths to weaponized Metasploit exploit modules, Nuclei YAML templates, and starred GitHub PoCs.
Quickstart
Clone the repository and inspect any CVE or query the database in milliseconds:
# 1. Inspect a specific CVE with full telemetry (CVSS, EPSS, KEV, PoCs, Metasploit, Debian fix):
python3 cve_search.py CVE-2024-3094
# 2. Check full database summary scoreboard:
python3 cve_search.py --statsDense Semantic Vector Search
Unlike traditional keyword search, semantic search understands natural language concepts. You don't need exact keywords—describe the security scenario and the system finds the closest vulnerabilities in under 300 milliseconds:
# Natural language search:
python3 cve_vector_search.py "pre-auth remote code execution in fortinet firewall" -n 5
# Search Linux kernel privilege escalation:
python3 cve_vector_search.py "ebpf kernel privilege escalation" -n 5
# Combine semantic search with threat intelligence filters:
python3 cve_vector_search.py "sql injection in authentication" --kev -n 5
python3 cve_vector_search.py "java untrusted deserialization" -m -n 5
# Integrated shortcut via main CLI:
python3 cve_search.py -V "vmware vcenter authentication bypass" -n 3Full-Text Keyword Search (SQLite FTS5)
Search across titles, descriptions, vendor products, and tool metadata using millisecond FTS5:
# Keyword search:
python3 cve_search.py -s "authentication bypass" -n 10
# Filter for active exploitation (CISA KEV):
python3 cve_search.py -k -s "cisco"
# Filter for ready Metasploit modules:
python3 cve_search.py -m -s "fortinet"
# Filter for ready Nuclei templates:
python3 cve_search.py -t -s "wordpress"
# Filter by high EPSS probability (e.g. >= 80%):
python3 cve_search.py --min-epss 0.8 -s "apache"SQLite Database Schema (cve.db)
The unified SQLite database (1.4 GB, WAL mode) contains 10 relational tables and a virtual FTS5 table:
| Table Name | Records | Primary Columns |
|---|---|---|
cves |
400,776 | id, title, description, cvss_score, epss_score, is_cisa_kev, has_exploit... |
cisa_kev |
1,730 | cve_id, vendor_project, product, required_action, due_date... |
epss_scores |
381,682 | cve_id, epss, percentile |
metasploit_modules |
3,521 | module_path, cve_id, name, rank, type, disclosure_date |
nuclei_templates |
4,509 | id, cve_id, name, severity, template_path |
github_pocs |
25,524 | cve_id, repo_name, repo_url, stars, forks, updated_at |
exploits |
46,689 | id, cve_id, title, file_path, platform, author |
debian_security |
71,525 | package_name, cve_id, scope, releases_json |
cwes |
969 | id, name, status, description |
Hugging Face Datasets Hub Publishing
The complete dataset is packaged into 8 partitioned Apache Parquet chunks ready for distribution on the Hugging Face Hub:
# Upload the entire dataset + Dataset Card to Hugging Face Hub:
export HF_TOKEN="hf_xxxxxxxxxxxxxxxxxxxxxxxxx"
python3 export/huggingface/publish_to_hf.py --repo-id "YOUR_USERNAME/cve-threat-intelligence-embeddings"Once published, anyone can load the dataset and embeddings in Python with a single line:
from datasets import load_dataset
ds = load_dataset("YOUR_USERNAME/cve-threat-intelligence-embeddings", split="train")
print(f"Loaded {len(ds):,} CVE records with 384-dim embeddings!")Daily Synchronization Engine (sync_all.py)
Update all feeds and rebuild SQLite in one command:
# Run full sync:
python3 sync_all.py
# Fast sync (skipping heavy git repos, updating daily EPSS, KEV, tools):
python3 sync_all.py --skip-repos --skip-osv
# Fast DB re-index (only new threat feeds, takes ~15s):
python3 scripts/build_db.py --only-newAI Agent Integration (AGENTS.md)
Equip coding assistants (Claude Code, Antigravity, Cursor, Codex) with instant vulnerability lookup by pointing them to AGENTS.md or adding GLOBAL_AGENT_RULE.md to your agent prompt.